A Loan-Shark Gang in Kumanovo Ran for Five Years - and Only Fell When One Citizen Found the Courage to Report It
06.11.2026


06.11.2026

06.11.2026

06.11.2026

06.11.2026
06.11.2026

06.11.2026

06.11.2026
05.11.2026

05.11.2026
06.11.2026
06.11.2026

05.11.2026
06.11.2026
06.11.2026

06.11.2026
06.11.2026
05.11.2026
04.11.2026
06.11.2026

06.11.2026
06.11.2026
06.11.2026
05.11.2026
05.11.2026
06.11.2026

05.11.2026
04.11.2026
23.04.2026
23.04.2026
12.04.2026
DreamHost, an American web hosting company, has confirmed that hackers stole customers' emails and login data in an attack that lasted for months. The attack began in August, and the company disclosed it only toward the end of October, after it caused an outage that lasted several days and during which some customers' passwords were reset.
According to the data breach notice the company filed with the California attorney general, the attackers obtained session tokens - the small digital keys that keep you logged in after you have already entered your password. With a stolen token, a hacker walks into the system as if they were the user. They got in through an unnamed vulnerability in DreamHost's file manager, exactly the place where customers keep their files.
That is where the answers stop. A company spokesperson declined to say why the attack went unnoticed until last week, citing the ongoing investigation. Nor did they say what the vulnerability is, other than that it has nothing to do with recently discovered flaws in PHP software. How many customers are affected? "Well under 10 percent," says DreamHost, and nothing more precise.
The company boasts about 400,000 paying customers. Ten percent of them is 40,000 people - that is the upper limit the company leaves open.
For months someone was reading other people's mail and searching through customers' files, and the firm that charges precisely for keeping those files safe is the last to find out. How many small businesses, including ones from the Balkans, keep their websites with foreign hosting companies - and how many of them would ever learn their mail had been opened, if the host didn't tell them itself?
The latest 10 news from this category
Brockman boasted of 70 percent revenue growth in a single quarter. How much that is in money, he didn't say.
Meta isn't hiding why its AI agent has a sweet face and gestures: so people feel connected to it. The...
A company founded in 2024, with a product launched last summer and agents borrowed from Anthropic and OpenAI - now...
Geoffrey Hinton isn't afraid of robots, he's afraid of the dark: power grids and banks down for days. And he...
The most popular AI companions have 220 million downloads, and many of them aim squarely at younger users. Apple now...
Half a metre of plastic, printed in orbit. Sounds modest, but the whole space industry keeps hitting one limit: everything...
Designed by the man who drew the iPhone, mocked at its premiere, sold out before the first delivery. When the...
Deeper in its IPO prospectus, in the risk section, Anthropic wrote that the development of the company's models may soon...
The Bundestag is counting potentially hacked phones, and Berlin won't say whether Merz was a target. The irony: German police...
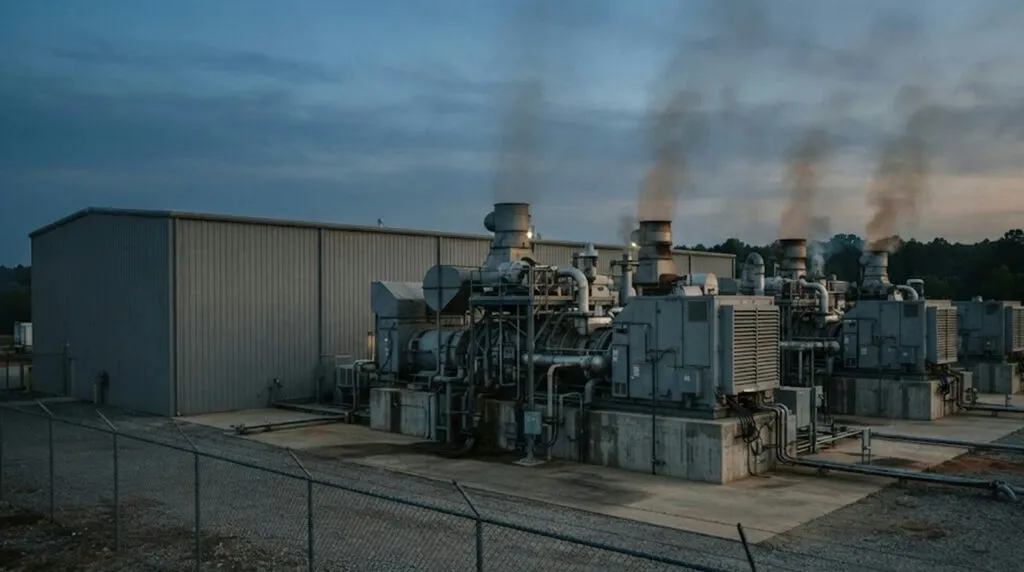
The SpaceX-owned company also argued citizens have no right to sue over the air they breathe. The court disagreed, and...
This site uses cookies - is that okay? Learn more
Be the first to know when Metla launches something new
Leave your email and we'll write to you when there's a new guide or something new on Metla.