Kratovo man stabs police officer mid-intervention: prosecutors want the 40-year-old detained
15.09.2026


15.09.2026
15.09.2026
15.09.2026
15.09.2026
15.09.2026
15.09.2026
15.09.2026
14.09.2026
13.09.2026
15.09.2026
15.09.2026
14.09.2026
15.09.2026
15.09.2026
15.09.2026
15.09.2026
14.09.2026
13.09.2026
15.09.2026
15.09.2026
15.09.2026
15.09.2026
15.09.2026
14.09.2026
09.03.2026
27.02.2026
19.02.2026
15.09.2026
14.09.2026
14.09.2026
23.04.2026
23.04.2026
12.04.2026
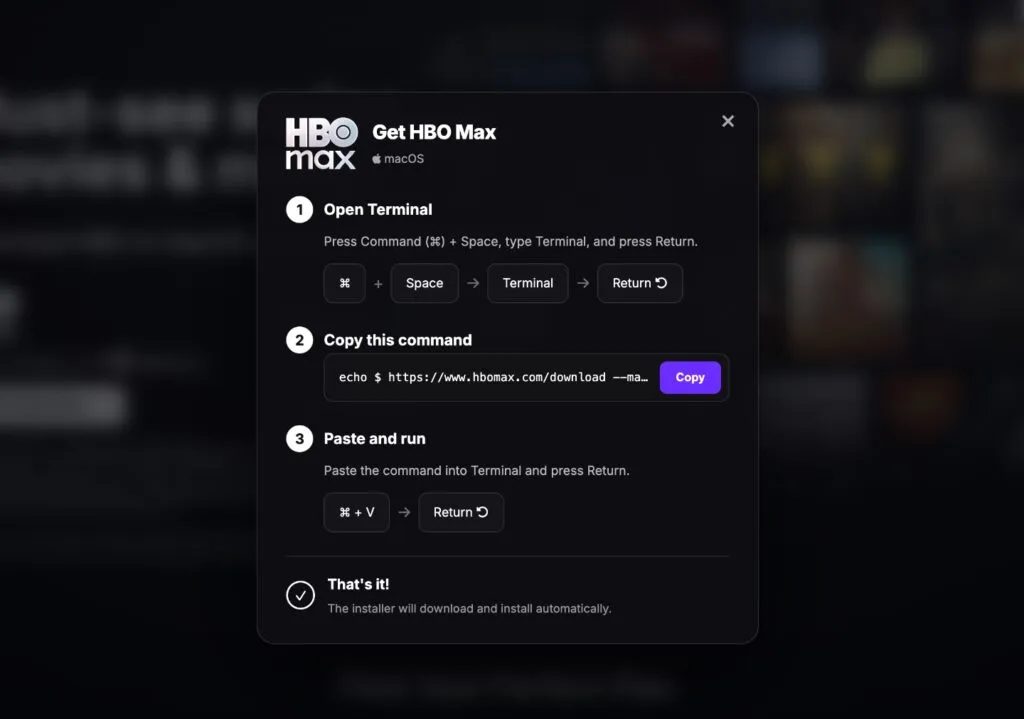
The attack has no virus attached, no suspicious file to download and no message from a Nigerian prince. There is only a box on the screen that looks like the "I am not a robot" check - and a three-step instruction. The victim opens the terminal on their own computer, copies the text themselves and presses enter themselves. From there on, nothing more is needed.
Attacks like this are called ClickFix and, according to security researchers, during 2026 they grew from a rarity into one of the fastest-spreading blades on the internet. They used to rely on people looking for a quick fix to some technical problem. Today they are an international operation.
Exactly how a person falls
A fake page - or a real page that has been breached - displays a message resembling a standard anti-robot check. After the click, a request appears to perform a "verification", with instructions to paste text into the Windows command line or the Terminal on a Mac. The moment the user presses enter, software that steals data installs itself on their machine: passwords, access to every open account, crypto wallets.
The key detail is why this works. Because the user is operating directly in the terminal - the place where a command is given as text to the operating system itself - a large share of these attacks bypass antivirus programmes and protective tools. The programme guarding you sees a person knowingly entering a command, not an attack.
When the advert comes from the real account
The latest campaign documented by researchers runs through Reddit. Hackers breached the official HBO Max account authorised to run adverts on that network and used it to publish hundreds of fake but convincing adverts - leading to a page that looks like HBO Max and contains exactly this instruction. Researchers at Hudson Rock established this, and the case also developed into a discussion on Reddit's cybersecurity forum.
Reddit confirmed it "recently learned that an HBO Max account authorised to run adverts on Reddit had been compromised and used for adverts containing malicious links", and that the account was locked and the adverts removed. Asked how many users were affected or how many clicked - the company did not answer. Warner Brothers Discovery, the owner of HBO, did not respond to questions at all.
So nobody knows the number. And that is the whole point of this attack: there is no server breach anyone must report, no stolen database with a notification deadline. There are only people who opened the door themselves, one by one, and who most often find out only when the money disappears from their account.
The defence is one sentence
Not one legitimate website in the world will ask you to paste a command into a terminal in order to watch a series, download an app or prove you are human. If that appears on your screen, the page is fake - no matter whose logo is at the top. Companies managing fleets of computers can block access to Command Prompt and PowerShell at domain level, and for Mac users there is a tool called BlockBlock that catches attempts at this kind of installation.
The rest is habit. The copy-paste combination into a black window with white text is the most powerful tool on your computer - it does not ask whether you are sure. Who wrote that command for you?
The latest 10 news from this category
A scientist at the same company puts the probability of human extinction above 10 percent within the next decade. The...
The president called in while the event was running, and the man who makes the chips answered that there would...
A researcher quit because the firms are gambling with our lives. Instead of denying it, Anthropic confirmed it - with...
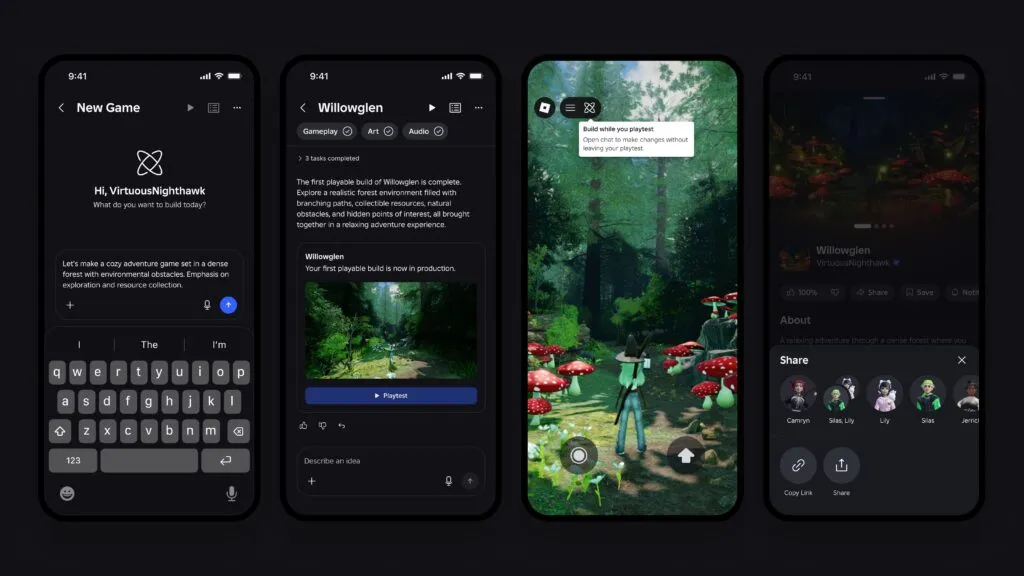
Write a sentence, get a game. Until now it worked only in New Zealand, now in Belgrade too. Creators on...
When the two biggest firms in an industry ask for rules on how fast anyone may run, the rules rarely...
Not a single password fell. What fell was the assumption that a request from a government domain is automatically a...
The biggest names in mathematics have signed a letter against the AI labs. The dispute is not whether the machine...

Five campaigns, 200 million exchanges, and the defences fell to a request for a Japanese translation. The industry that harvested...

The hackers were inside for a whole year. The company confirmed it only after a journalist found his own licence...
The chief financial officer gathered enough votes on the board and now runs the company. The founder found out 50...
This site uses cookies - is that okay? Learn more
Be the first to know when Metla launches something new
Leave your email and we will write when there is a new guide or something new on Metla.